Ransomware Protection
Immutable Backups and Ransomware Protection
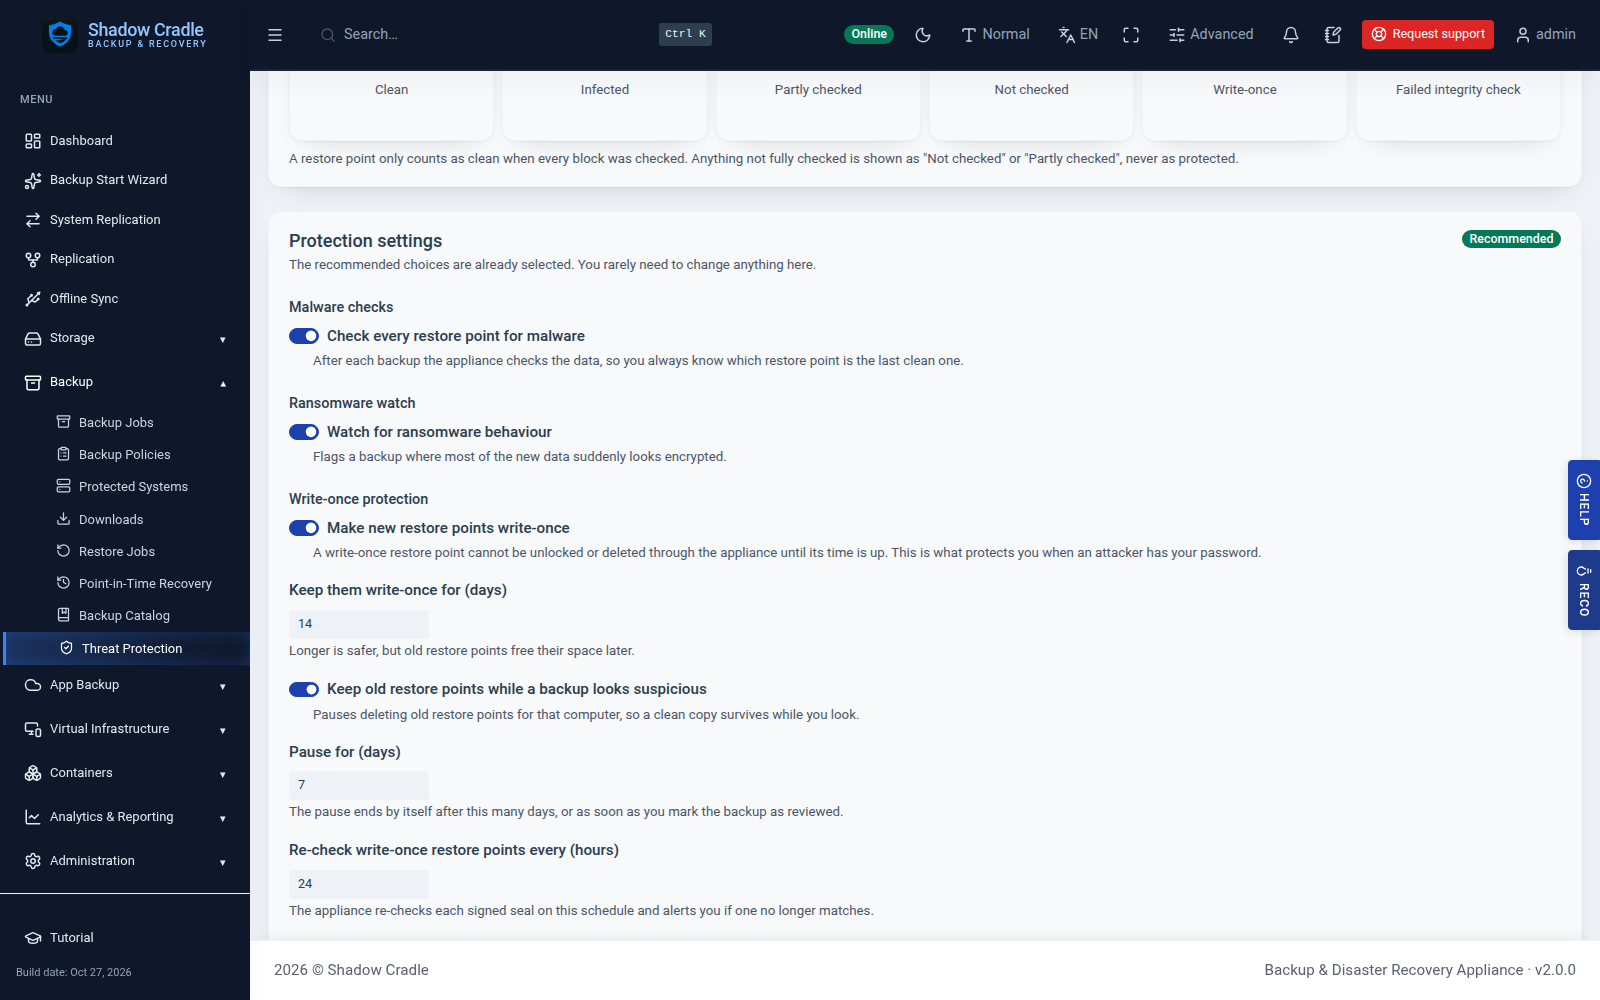
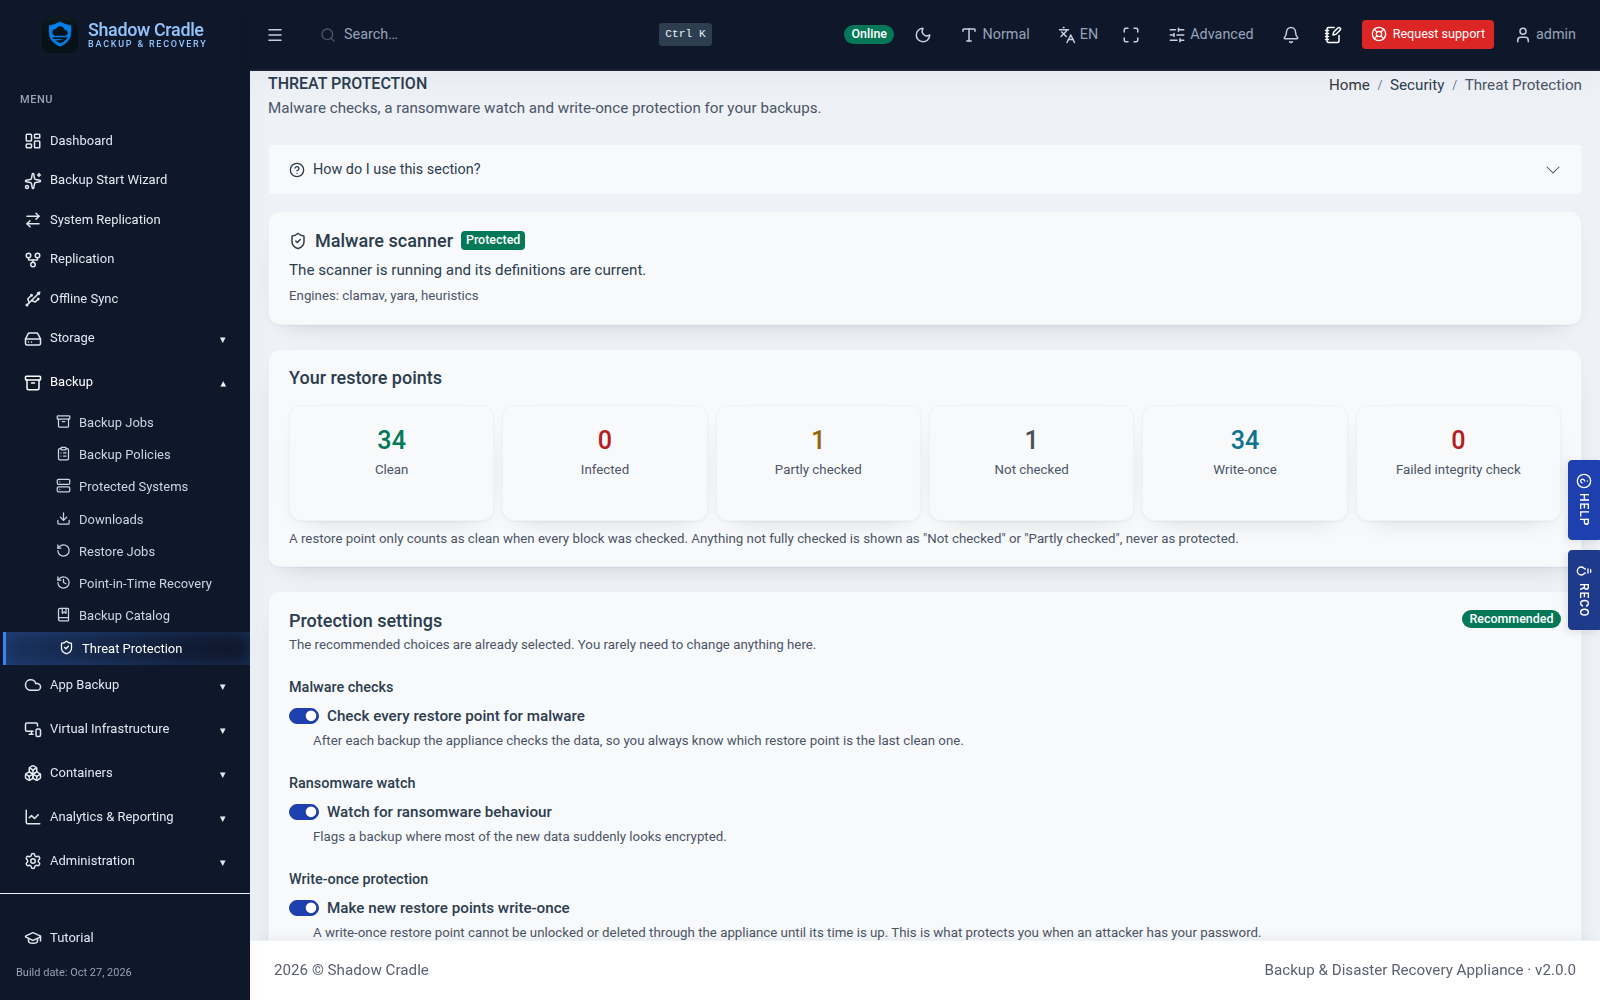
Seal restore points so they cannot be changed. Watch for unusual backup activity. Scan restore points before you restore them.
Write-once seals
Recovery bin
Anomaly detection
Pre-restore scan
Tamper-proof audit log
Keep Backups Safe
Write-once seals are enforced in software.
Write-once seals
A sealed restore point refuses unlock and delete until its window ends.
Recovery bin
Deleted items wait in a bin. You can place a legal hold on them.
Two-step delete
Deleting for good needs an emailed code, a 2FA code and a waiting period.
Tamper-proof audit log
Every change is logged with a before and after diff. Export it as CSV or JSON.
Spot Trouble Early
Anomaly detection
Tunable thresholds for backup size and file changes. Each alert has a score. You can acknowledge it or mark it a false positive.
Pre-restore scan
Scan a restore point for malware before you restore it. A sanitize option helps clean a restore.
Sentinel files
Agents watch decoy files on protected machines for signs of ransomware.
Inside the Appliance
Screens from the live demo with sample data.
Part of the Full ShadowCradle Platform
Data loss stops here
Write-once retention and self-healing storage engineered to make data loss the exception, not the outcome.
Backups that test themselves
Scheduled restore tests - recovery you've watched work.
Audit-ready by default
Reports to support HIPAA · SOC 2 · GDPR work, from the dashboard. Not a certification.
A team behind every deployment
Real engineers on the line, with fast follow-up.